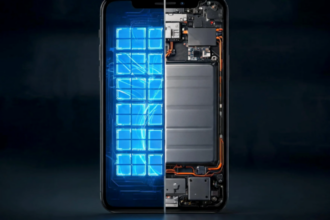


The digital landscape is undergoing a tectonic shift. For decades, the password has been the gatekeeper of our online existence, a flawed relic of early computing that has become the primary vector for data breaches. You are likely being prompted by every major website to switch to a passkey, and if you feel a sense of hesitation or confusion, you are not alone. While mainstream media often frames the passkey vs password debate as a simple upgrade, they frequently gloss over the profound friction that users face when transitioning to this new standard.
- The Singpass Lesson: Why governments are leading the way
- The “Sealed Box” comparison: Passkey vs Password explained simply
- Table 1: Operating Mechanisms and Real-World Risks in the Passkey vs Password Debate
- Addressing the “Ugly Truth” that tech media hides
- Table 2: User Pain Points and Practical Experiences in Passkey vs Password Adoption
- Why user frustration is actually valid
- The transition strategy: How to survive the change
- The reality of the modern threat landscape
- Why you don’t need a computer science degree to use passkeys
- The critical role of biometrics
- Is it time to ditch passwords?
- Moving toward a passwordless future
- A note on the technical friction
- The importance of standardizing recovery
- Looking ahead: The long-term impact of the shift
- Conclusion
While the tech media often frames this change as a simple upgrade, they frequently gloss over the profound friction that users face when abandoning a system they have relied on for thirty years. This shift is not merely a corporate marketing push; it is a fundamental reaction to an internet that is no longer safe for traditional secrets. When evaluating the security implications, it becomes clear that the old way is failing, making this transition an urgent necessity for the modern user.
The Singpass Lesson: Why governments are leading the way
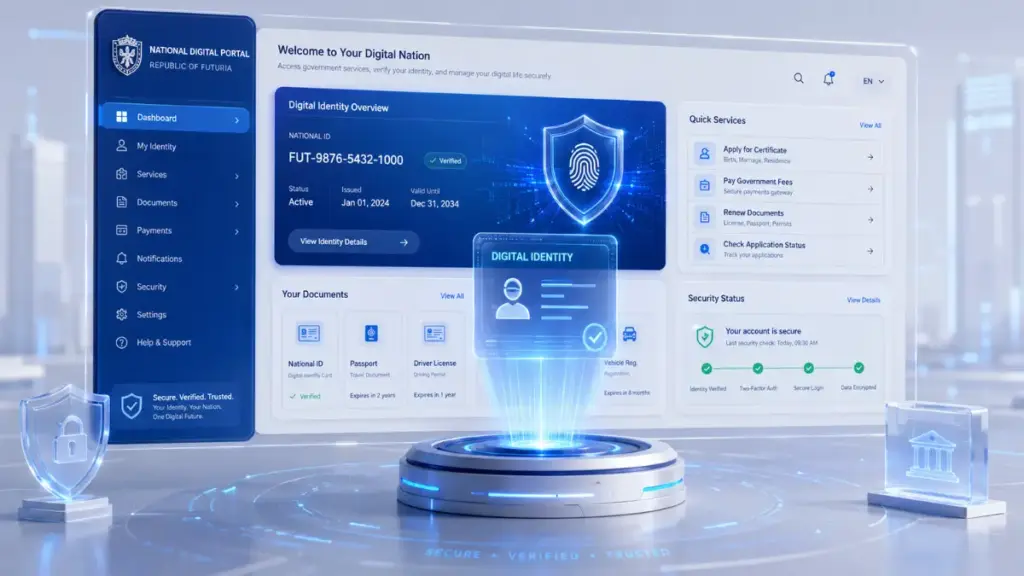
In Singapore, the government successfully transitioned citizens to the Singpass system, effectively relegating traditional credentials to the past for public services. This is not merely a corporate marketing push; it is an infrastructure-level necessity. By removing the vulnerable text-based secret from the equation, Singapore has drastically reduced successful phishing attacks against its citizenry.
This transition serves as a “stress test” for the rest of the world. It proves that when the stakes involve national infrastructure, taxation, and healthcare, the reliance on human-memorized strings of characters is a vulnerability that no longer holds up under modern threat models.
The “Sealed Box” comparison: Passkey vs Password explained simply
To move past the confusion, we must stop using the jargon of computer science and start using mechanics we understand. The passkey vs password comparison often fails because it focuses on the math rather than the logic of ownership.
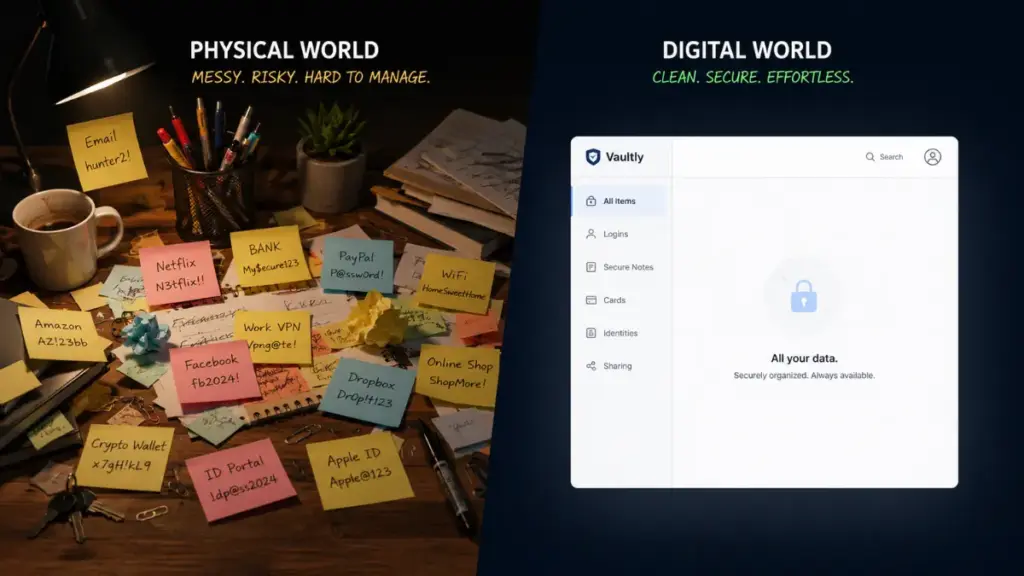
The old way: The paper-and-padlock model
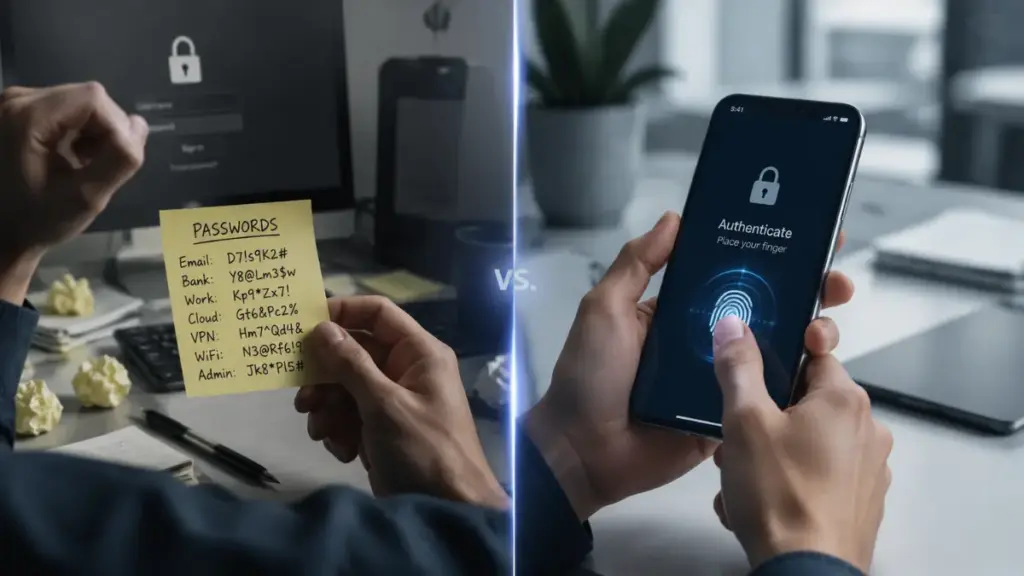
Imagine you have a secret code written on a piece of paper. To log into a website using the traditional passkey vs password model, you hand this paper to a guard (the server). The guard places your paper in a massive vault alongside thousands of others. If a thief breaks into the vault, your paper—and everyone else’s—is stolen. Because humans are forgetful, we use the same paper for everything. If one vault is breached, your entire digital life is compromised, a risk the passkey vs password upgrade specifically mitigates.
The new way: The digital seal
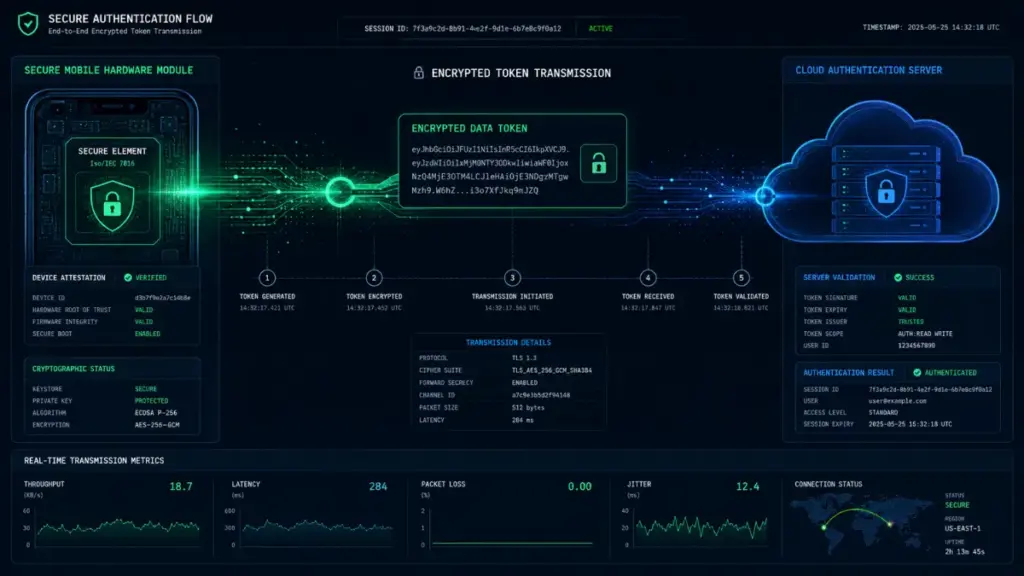
A passkey is a digital seal. You don’t hand over your secret; you keep it entirely on your device. When you interact with a website, your device “stamps” a unique, time-sensitive signal. Crucially, this seal is cryptographically bound to the specific URL. If you accidentally visit a fake site—like “g00gle.com” instead of “google.com”—your device will notice the discrepancy and refuse to provide the seal, proving the superiority of the passkey vs password authentication logic.
“Passkeys are essentially a unique, digital fingerprint for every site. They don’t leave your device, meaning even if a website’s database is fully compromised, there is nothing for the hackers to steal.”
Luna
Table 1: Operating Mechanisms and Real-World Risks in the Passkey vs Password Debate
| Feature | Password | Passkey |
| Storage Mechanism | Centralized server | Secure local device storage |
| Phishing Resistance | Low; susceptible to look-alike domains | Absolute; bound to legitimate domain |
| Data Breach Impact | High; server leaks expose all users | Negligible; no secret on the server |
| Secret Integrity | Vulnerable to dictionary/brute force | Secure; uses asymmetric cryptography |
| Authentication Logic | Knowledge-based (what you know) | Possession-based (what you hold) |
| Transferability | High; easily shared or stolen | Low; device-locked or secure cloud |
| Key Generation | Human-selected (often weak) | System-generated (high-entropy) |
Read more: Passkeys: 7 Dangerous Realities Big Tech Won’t Tell You Before You Switch.
Addressing the “Ugly Truth” that tech media hides
The tech industry rarely addresses the “dependency trap” within the passkey vs password discussion. When you move to a passkey-first workflow, you are essentially betting on the longevity and security of your cloud provider.
The dependency trap
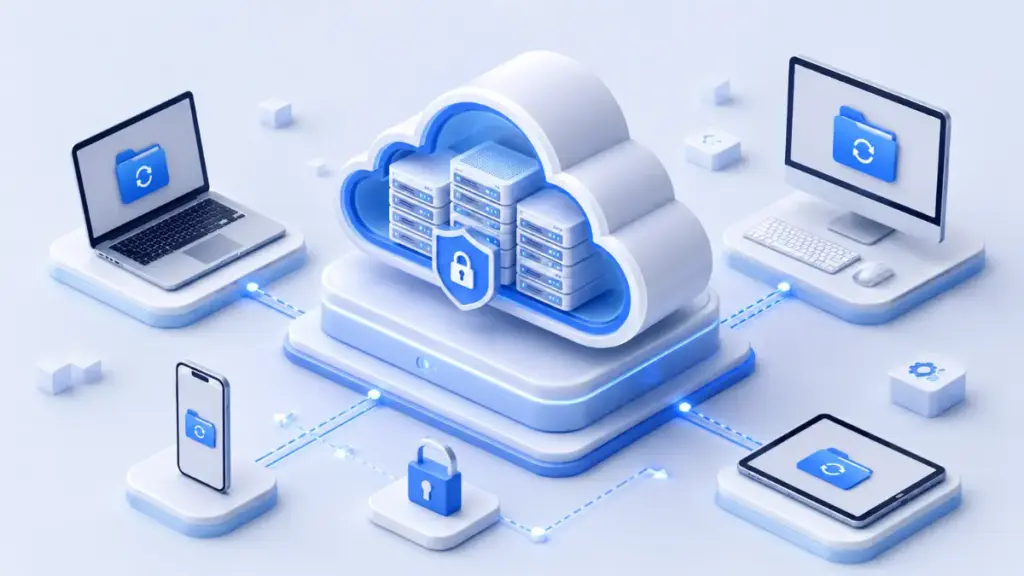
If your passkeys are synced through a provider like iCloud or Google, you are tethered to that ecosystem. While this provides the convenience of moving between devices, it also creates a single point of failure in the passkey vs password landscape. If your main account is locked, the ability to recover your digital identity becomes significantly more complex than simply resetting a password.
The “Work/Public Computer” nightmare
Users frequently ask: “How do I log in when I’m at the office?” This is where the passkey vs password comparison hits its biggest snag. Passkeys are designed for your personal devices. Logging in on a “third-party” computer requires a multi-step process—often involving a QR code scan. It is objectively more secure, but it is also objectively more cumbersome than the old passkey vs password standard of typing a string.
“The goal is a future where your digital existence is as protected as your physical bank vault, but as easy to access as unlocking your phone.”
Luna
Table 2: User Pain Points and Practical Experiences in Passkey vs Password Adoption
| User Experience Challenge | Traditional Password | Passkey |
| Initial Setup Effort | Easy (typing a string) | Moderate (requires device pairing) |
| Cross-Device Syncing | Easy via browsers | Complex (requires ecosystem support) |
| Public Computer Login | Fast but insecure | Slower (requires phone/QR scan) |
| Changing Phones | Seamless (just log in) | Requires migration of secure data |
| Office/IT Policies | Simple (managed by IT) | Difficult (requires device control) |
| Account Recovery | Email-based (very insecure) | Identity-based (very secure/difficult) |
| Daily Login Speed | Depends on memory | Instant via biometrics |
Why user frustration is actually valid
When users complain that they “don’t want to be computer scientists,” they are voicing a legitimate grievance against the lack of transparency in the passkey vs password transition. The industry often treats these security changes as “obvious” improvements, ignoring the fact that for a regular user, changing how they pay their utility bills is a high-stress event.
The complexity of terms like “asymmetric encryption” or “hash functions” is not merely technical—it is exclusionary. To make the passkey vs password standard successful, the industry needs to focus on the UX of recovery. If the recovery process is not as seamless as the login process, we are setting millions of users up for a permanent lockout.
The transition strategy: How to survive the change
Do not attempt a “big bang” migration where you try to convert every account at once. That is a recipe for disaster in the passkey vs password era.
- Start with the high-stakes, low-friction accounts: Start with the high-stakes, low-friction accounts: Your primary email and banking are the safest places to start. These are usually well-supported in any modern authentication implementation.
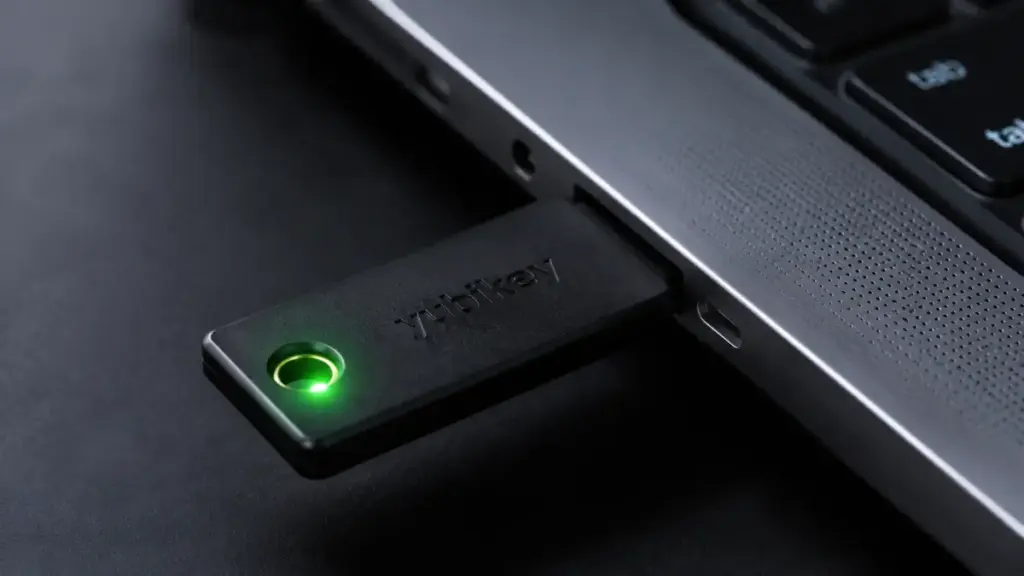
- Establish a backup protocol: Do not rely on one single device. If you use a manager, ensure it supports the new security standard and is synced across at least two different platforms.
- Document your recovery paths: Before deleting a traditional credential for a critical service, look for the recovery options provided by the site. If they only allow email recovery, keep your email as a primary credential for a while longer during your migration.
The reality of the modern threat landscape
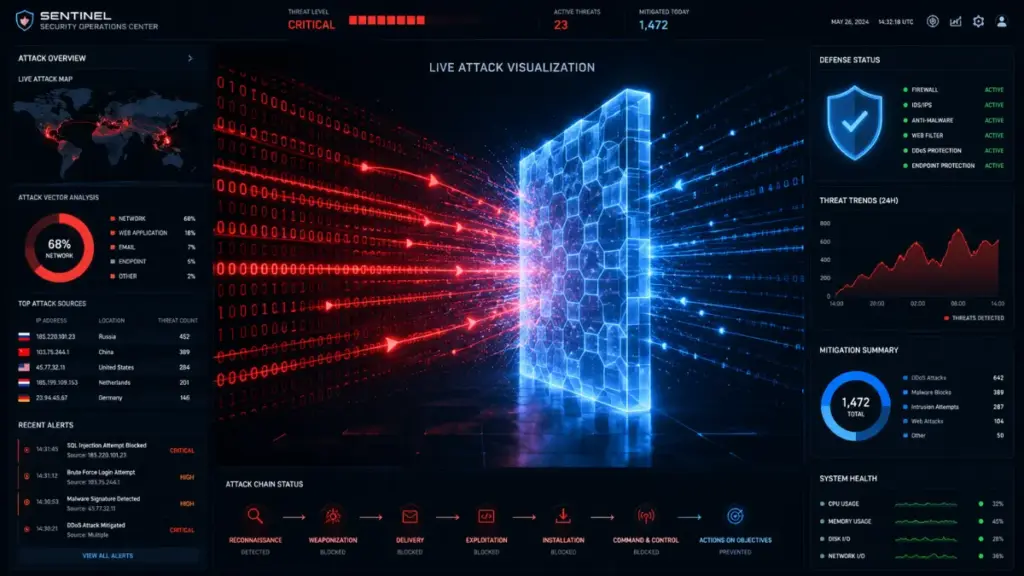
The persistent push for passkey vs password is fundamentally about the changing nature of the threat. We are no longer dealing with amateurs trying to guess “123456.” We are dealing with sophisticated, automated phishing campaigns that can scrape credentials from real-time web sessions. This is why the passkey vs password security shift is vital.
Traditional passwords are data points. They can be intercepted, stored, and sold on the dark web. A passkey is an action. It is a one-time event. Because there is no “secret” stored on the server to intercept in a passkey vs password ecosystem, the attacker’s main weapon—the data breach—is rendered useless.
Why you don’t need a computer science degree to use passkeys
You do not need to understand how the internal logic of a car works to drive one. The same applies here. The browser handles the complex handshake between the “public key” (on the website) and the “private key” (on your device).
More Read
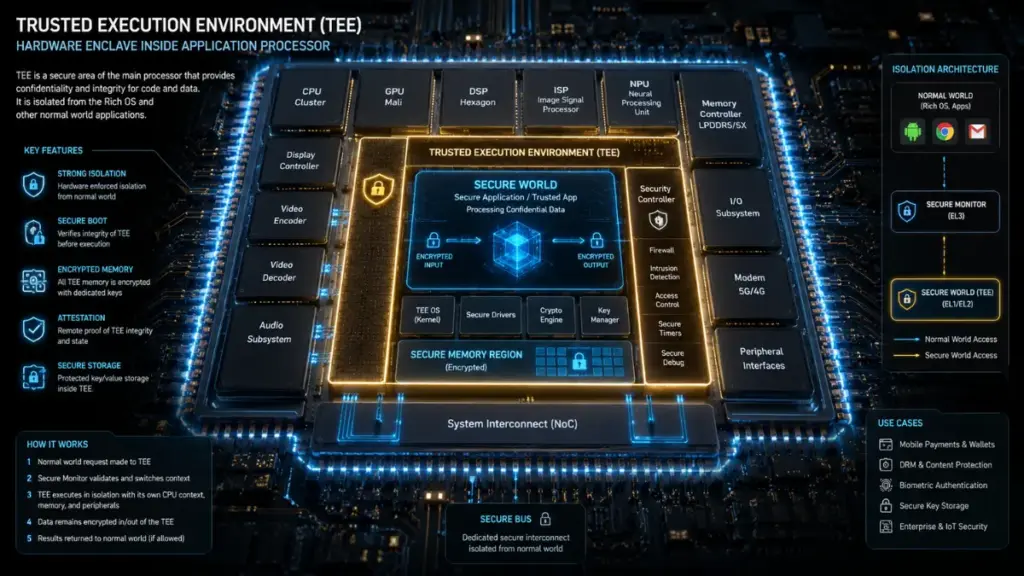
The industry has done a poor job of explaining that the passkey vs password migration is not about adding more work for you—it is about moving the work to the hardware. Your device’s secure enclave does the heavy lifting, protecting the key so effectively that even if your phone is infected with malware, the key remains isolated and inaccessible, which is a core benefit of the passkey vs password architecture.
The critical role of biometrics
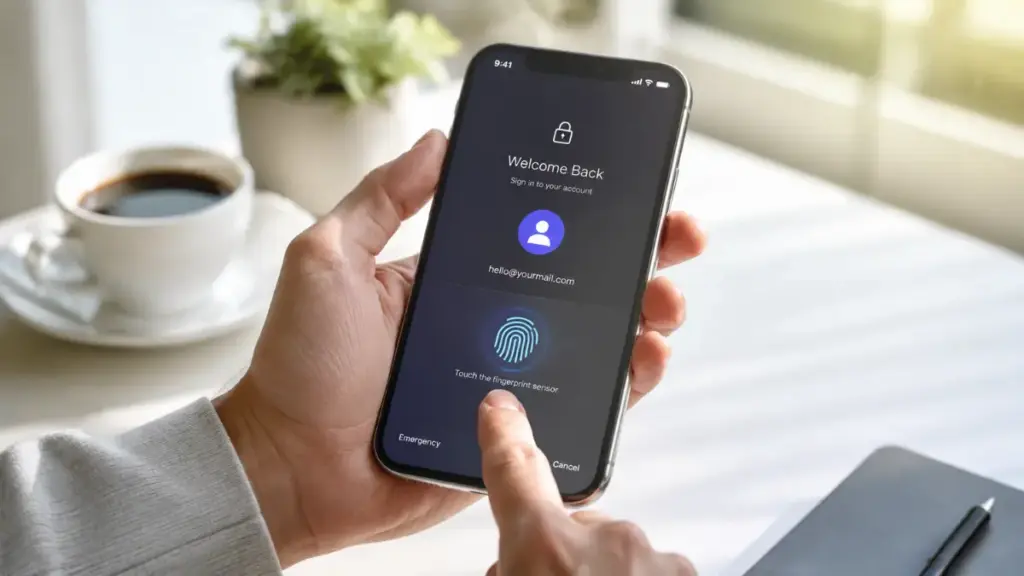
We cannot discuss passkeys without discussing the biometric barrier. Biometrics (FaceID, fingerprint) serve as the local gatekeeper for your passkey.
Some users fear that their face or fingerprint is being sent to the website. This is a fundamental misunderstanding in the passkey vs password debate. Your biometric data never leaves your device. The website is simply told “the user has successfully verified their identity locally.” The website never sees your face, nor does it receive your biometric scan. This decoupling of identification and authentication is the crowning achievement of this new passkey vs password standard.
Is it time to ditch passwords?
For the vast majority of users, the answer is a qualified “yes.” While the passkey vs password transition brings legitimate logistical challenges, the risk of remaining on the password-centric model is significantly higher. The industry is reaching a consensus: passwords are a liability.
However, move at your own pace. The frustration expressed by users in online forums regarding the passkey vs password shift is not a sign that the technology is flawed; it is a sign that the implementation and communication have been rushed. Take control of your recovery protocols, use a trusted hardware-backed manager, and treat your digital identity as a professional asset rather than a forgotten string of characters in the passkey vs password landscape.
Moving toward a passwordless future
We are witnessing the end of an era. The password has served us for nearly forty years, but it has reached its breaking point. As we continue to integrate more of our lives—from banking to government services—into the cloud, the cost of a compromised credential becomes too high in the passkey vs password era.
The passkey vs password transition is not merely a change in login style; it is a fundamental shift in how we conceive of ownership over our digital selves. By moving away from “shared secrets” and toward “local authentication,” we are reclaiming some of the autonomy that we lost in the early days of the internet via this new passkey vs password framework.
A note on the technical friction
We must acknowledge that the friction is not entirely in your head. The current passkey vs password landscape is fragmented. You have some websites that support it, some that don’t, and some that try to force you into their proprietary apps. This messiness is a temporary symptom of a transition.
When we look back at the shift from physical cash to digital banking, there was a similar period of confusion and distrust. Today, we don’t think twice about paying for coffee with a phone. The same will eventually be true for the passkey vs password authentication standard.
The importance of standardizing recovery
The final piece of this puzzle is the standardization of account recovery. If the industry wants us to fully commit to the passkey vs password paradigm, they must build universal, predictable recovery paths that do not involve “calling the support line.”
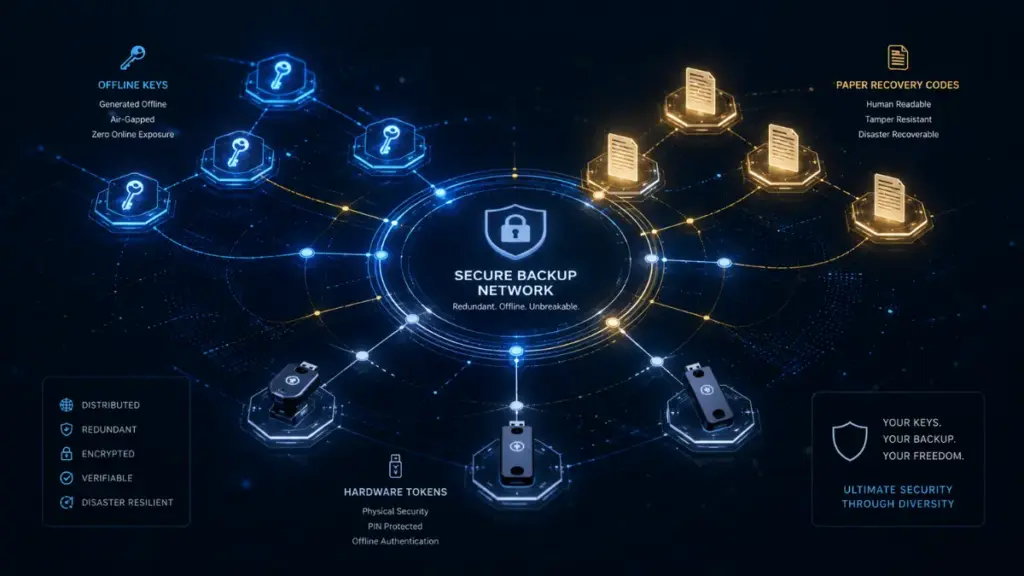
Until that happens, your best defense is your own foresight. Create your offline backups, maintain your hardware security keys, and ensure that your recovery emails are locked down with the highest possible level of security in the passkey vs password age.
Looking ahead: The long-term impact of the shift
In the long run, the shift to passkeys will likely lead to a reduction in the massive, economy-wide losses caused by credential theft. Phishing, which currently drains billions from unsuspecting users, will become significantly less effective due to the passkey vs password security improvement.
The goal is a future where your digital existence is as protected as your physical bank vault, but as easy to access as unlocking your phone. It is a high bar, and we are not quite there yet, but the trajectory of the passkey vs password shift is clear.
Conclusion
The evolution from traditional passwords to passkeys is as inevitable as it is challenging. By understanding the underlying mechanics—the “Sealed Box” of authentication—you can move through this transition with confidence. While the industry has been poor at communicating the benefits and managing the risks, the path forward is clear. Prioritize security, manage your own recovery, and embrace the passkey vs password change as a tool to protect your digital independence.
LEAVE A COMMENT TO GET FREE ADVICE FROM AN EXPERT OR FOLLOW OUR WEBSITE THE COUCH INSIDER FOR THE LATEST UPDATES.